Key takeaways
- Cybersecurity attacks have significantly increased, putting businesses at heightened risk.
- Bug bounty programs originated in the 1980s and have evolved into effective crowdsourcing initiatives.
- Major tech companies are now implementing bug bounty programs to identify vulnerabilities more efficiently.
- These programs help discover talented cybersecurity researchers and improve the security of software.
 Over the past few years, the number of cybersecurity attacks have increased significantly. Today, every single aspect of a business is under attack by hackers. As the world continues to become more digital with new mobile apps and other platforms, the risk of getting pwned is also increasing.
While companies are taking every possible step to secure all their platforms, hackers are also strengthening their attacking skills. And sometimes it gets difficult for a company’s in-house team to find and fix all the bugs. This is where bug bounty comes into the scenario.
What Is A Bug Bounty Program
The idea of bug bounty started back in 1983, when there was an initiative for Versatile Real-Time Executive operating system — the deal was that anyone who would report a bug would receive a Volkswagen Beetle (a.k.a. Bug) in return. Today, Bug bounty programs have reached a whole new level, it has completely become a crowdsourcing initiative that reward experienced independent researchers upon identifying and reporting on bugs or vulnerabilities in technology and software programs. Currently, even some of the big companies have started their own bug bounty program — Facebook, Uber, Apple, Intel etc. The effectiveness of the bug bounty program to identifying vulnerabilities early on is significantly high. You not only able to discover some of the best talents from the cybersecurity domain but also manage to increase the chances of finding some serious flaws and get them fixed.Some Of The Big Investments On Bug Bounty
Some of the big names that are going big on bug bounty programs are Intel, Snapchat, Facebook, Google, Apple etc.- Officially launched in September 2014, Microsoft Bug Bounty is also one of the high paying bug bounties. The company rewards a minimum of $15,000 and a maximum of $300,000. However, it is only for critical and important vulnerabilities.
- According to Intel’s Bug Bounty Program page, the company rewards bug bounty hunters a bounty from $500 to $100,000 USD depending on the nature of the vulnerability and quality & content of the report.

- Snapchat is in the race to make the best out of bug bounty programs. The company rewards a bounty from $2000 to $15,000. However, the company is currently focusing on some specific areas.
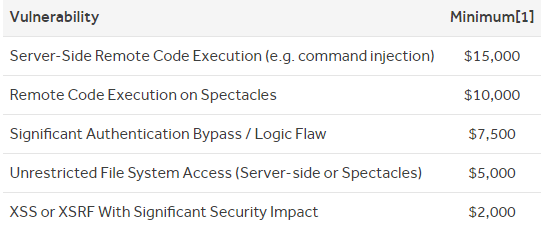
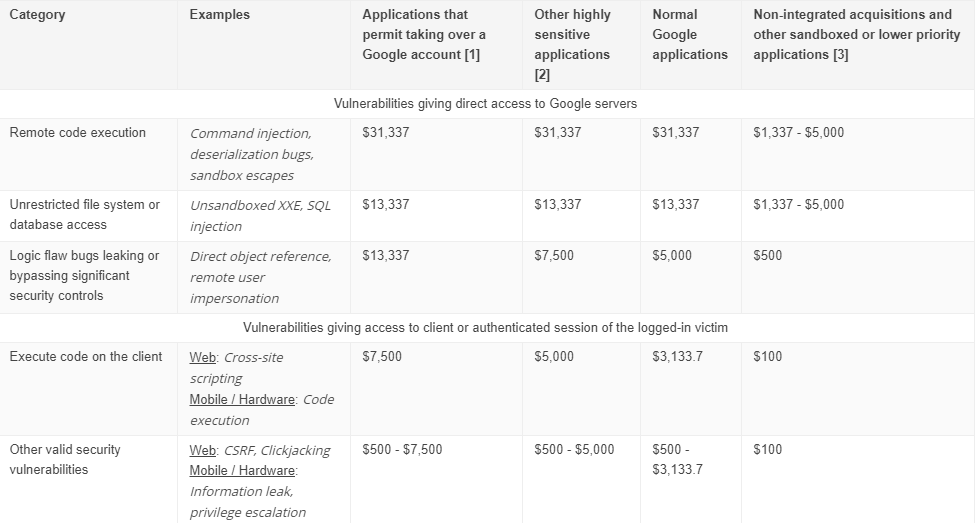
- Since November 2010, MountainView search giant Google has been running is Bug bounty program. And it is mostly focused on google.com, youtube.com, blogger.com. Talking about money, Google bug bounty rewards for qualifying bugs range from $100 to $31,337.
- Facebook runs one of the best bug bounty programs. Even though the company is always on the radar when it comes to data security, the social media tech giant has taken necessary measures to keep its platform safe. Facebook’s bug bounty program rewards successful hackers a bounty of minimum $500 and the maximum depends on the severity of the flaw. Click here to know more about the program.