
Cybersecurity firm CloudSEK found a threat actor named ‘rose87168’ allegedly selling six million records extracted from Oracle Cloud on March 21. The data included Java KeyStore (JKS) files, encrypted Single Sign-On (SSO) passwords, key files, and enterprise manager JPS keys.
The firm suggested a possible undisclosed vulnerability on login.(region-name).oraclecloud.com, which led to unauthorised access and the data breach.
However, Oracle denied the breach in a statement shared with Dark Reading.
In response, CloudSEK followed up with additional information to validate their initial theory of a possible breach.
“We believe there was a lack of judgment at the end of Oracle, and we intend to publish more details that would help the community and Oracle to investigate the incident better. At CloudSEK, we believe in transparency and evidence-based validation—not to create panic, but to enable preparedness, which we have been doing for the last 10 years,” they stated.
CloudSEK revealed that the threat actor was able to share a 10,000-line sample list of customer details and evidence of the attack by uploading a file created on ‘login.us2.oraclecloud.com’ and archiving the public URL with the attacker’s email within the text file.
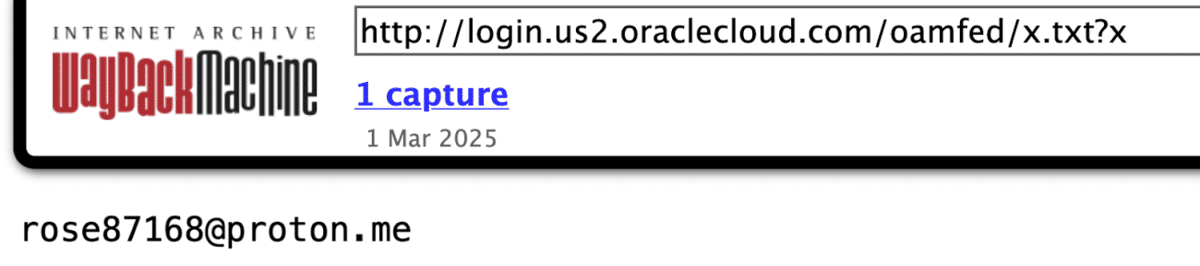
The firm did a background check on the server, validating the threat actor’s claim, which was taken down by Oracle a few weeks before the breach. As per the analysis shared, CloudSEK confirmed that the sample data included actual Oracle Cloud customers and not dummy users. Moreover, they confirmed that the domain in question was a production SSO setup.
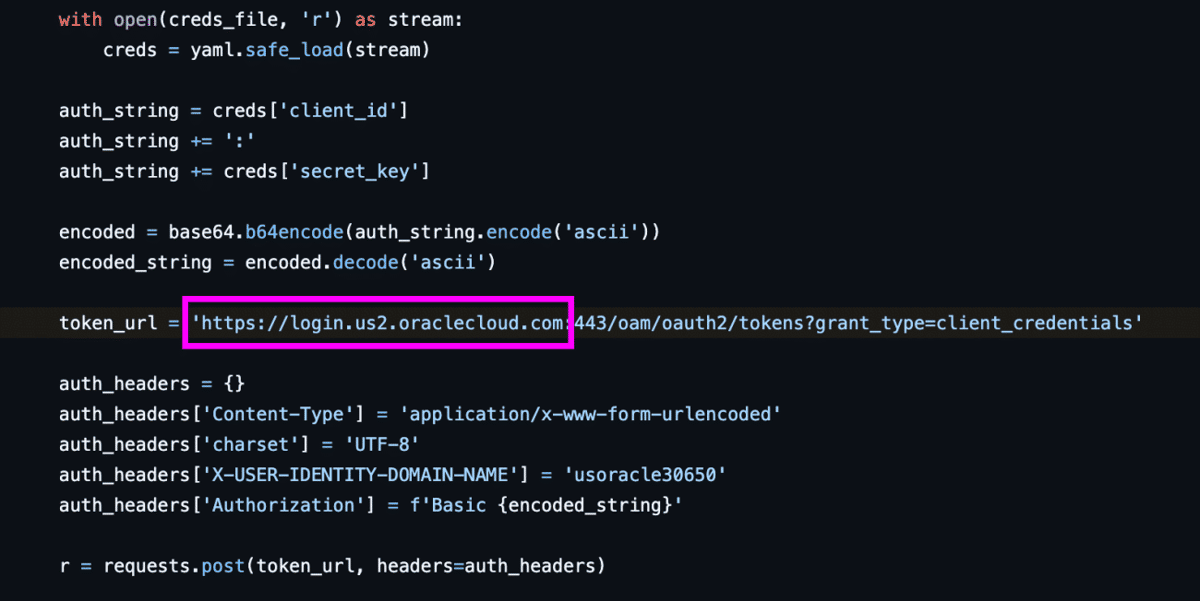
Some independent security researchers also reached a similar conclusion.
CloudSEK stated that the breach potentially impacts over 1,500 unique organisations and can lead to increased risk of unauthorised access and corporate espionage, along with financial and reputational risks.
The firm and security experts continue to monitor the situation and encourage Oracle to take action by disclosing more details.
- Anthropic Seeks Up to $64.4 Bn at $1.4 Tn Valuation With IPO
- IBM Ends H-1B, Green Card Sponsorship for Most Roles in Consulting Division
- PuppyGraph Raises $10 Mn to Help AI Agents Query Enterprise Tables
- Cognizant Commits 25,000 Professionals to Deploy Claude in Enterprises
- TSMC October Revenue Hits Record $17.81 Bn on Skyrocketing AI Chip Demand
- Froncort.AI Gets $2.3M From Google.org to Expand AI-Based Disease Screening in India