
5 min
 Whether you talk about building software or finding vulnerabilities in an existing platform, Indians over the years have marked their territory in the technology space and now hacking as a hobby has gained prominence with India having the highest base of white hat hackers. According to a recent report, bug hunting has proven to be 16x more lucrative than a job as a software engineer. A May 2017 Hacker Powered Security report indicated that white hat hackers in India got a whopping $1.8M in bounties.
In 2016, Facebook, on completing five years of its bug bounty program, posted an article and listed the top three countries based on the number of payouts of the bug bounty program and India topped the list.
Over the years, bug bounty programs have gained tremendous popularity in India and today, these programs are not only rewarding security researchers but also creating an ecosystem of knowledge sharing.
Here Is A List Of Indian Bug Bounty Programs That Every Security Researcher, Penetration Tester, or Security Engineer Should Try
OLA Bug Bounty Program
Indian origin cab services company Ola is one of the most rewarding companies when it comes to bug bounty. In order to encourage cybersecurity enthusiasts to find security vulnerabilities in OLA software, the company has a Security Bug Bounty Program. Also, upon successful reporting of security vulnerabilities, OLA rewards the security researchers based on the severity, impact and complexity of the vulnerability. The program is focused on the companies both core and other domains. The bug hunters will have to find carry out their work on only on the following domains: Core OLA: *.olacabs.com and *.olamoney.com Other Domains: Ola Cabs mobile app ( Android, iOS, and Windows ), Ola Lite mobile app (Android), Ola Money mobile app (Android and iOS), Ola Operator mobile app (Android), and Ola Partner mobile app (Android). To qualify for the bug bounty program, rewards, and Hall of Fame, one must meet the OLA’s prerequisite conditions:- You have to be the first to report the bug.
- One must adhere to the company’s responsible disclosure & reporting guidelines.
- The Bug bounty is only applicable to individuals.
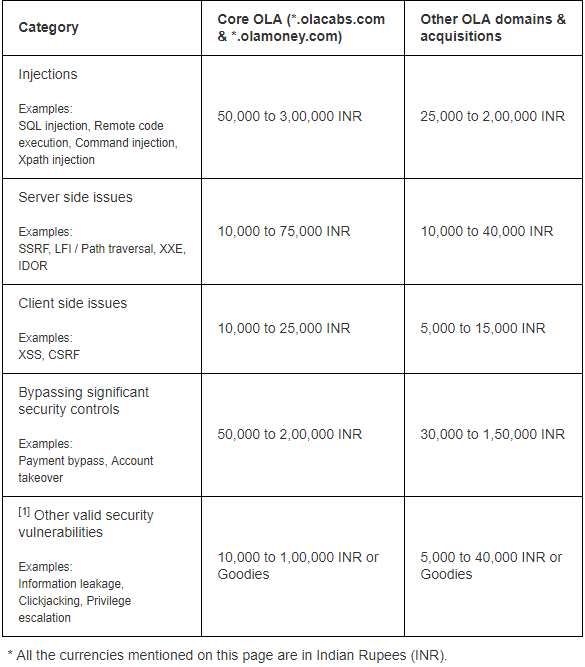 Source: https://www.olacabs.com/whitehat?[/caption]
For more information on other protocols of the OLA Security Bug Bounty Program, visit here.
McDelivery Bug Bounty Program
Another bug bounty program that every white hat should try is McDonalds India’s “Bug Bounty Program”. With a vision to encourage security groups or individual researchers to help to identify any potential security flaw in McDonalds India’s (i.e. Hardcastle Restaurants Private Limited (HRPL) Web and Mobile Application platforms for McDelivery, the company has started its own bug reporting program. The program is focused on the following domains:- McDelivery Web Application (www.mcdelivery.co.in);
- McDelivery Mobile Application (Android and iOS)
- McDelivery APIs
- Infrastructure Security
Paytm Bug Bounty Program
When it comes to bug bounty, the Indian e-commerce payment system and digital wallet company Paytm is also one of the active ones. In order to make all its platforms safer for its customers, the company allows independent security groups and individual researchers to perform vulnerability checks on all its platforms. When you find a bug, all you have to do is fill this Form. Word to the wise: When reporting a bug, make sure that you include as much information as you can (such as videos, PoC, screenshots etc.) Paytm’s bug bounty program focuses on the following domains:- *.paytm.com
- *.paytmmoney.com
- *.paytmmall.com
- *.paytmbank.com
- *.gamepind.com
- *.paytm.in
Yatra's Bug Bounty Program
Yatra is one of India's leading online travel portals, and in order to deliver its customers a more secure and safe experience on its platform, the company has a bug bounty program that invites bug hunter, security researcher, or a white hat hacker to find bug and flaws on its platform. The company is not only providing an opportunity for security enthusiasts to show their skills in identifying security vulnerabilities but also rewarding them with in return. When you find a bug or a vulnerability on Yatra’s platform that is exploitable, you have to report to by filling their report issue form (here is the link). Once you are done reporting the issue, Yatra’s security team investigates the issue and resolve it within a reasonable time frame. Upon successful and legit bug reporting, the company rewards the candidate with a monetary bounty (bounty is based on the bug’s severity, complexity, and impact). Talking about the domains, the program completely focuses on:- Yatra’s official website (www.yatra.com)
- Our mobile sites (Android & iOS)
- Our mobile apps (Android & iOS)

Your reaction
Discussion
What's your take on this story?
No comments yet — be the first to share your view.