
As AI becomes deeply embedded in daily life, personal data flowing through digital tools has reached an intimate scale. Food delivery apps know eating habits, streaming platforms understand entertainment preferences, payment apps map spending patterns, and AI assistants increasingly understand emotions, intent, and behaviour.
However, the increasing closeness between users and technology is triggering serious trust concerns.
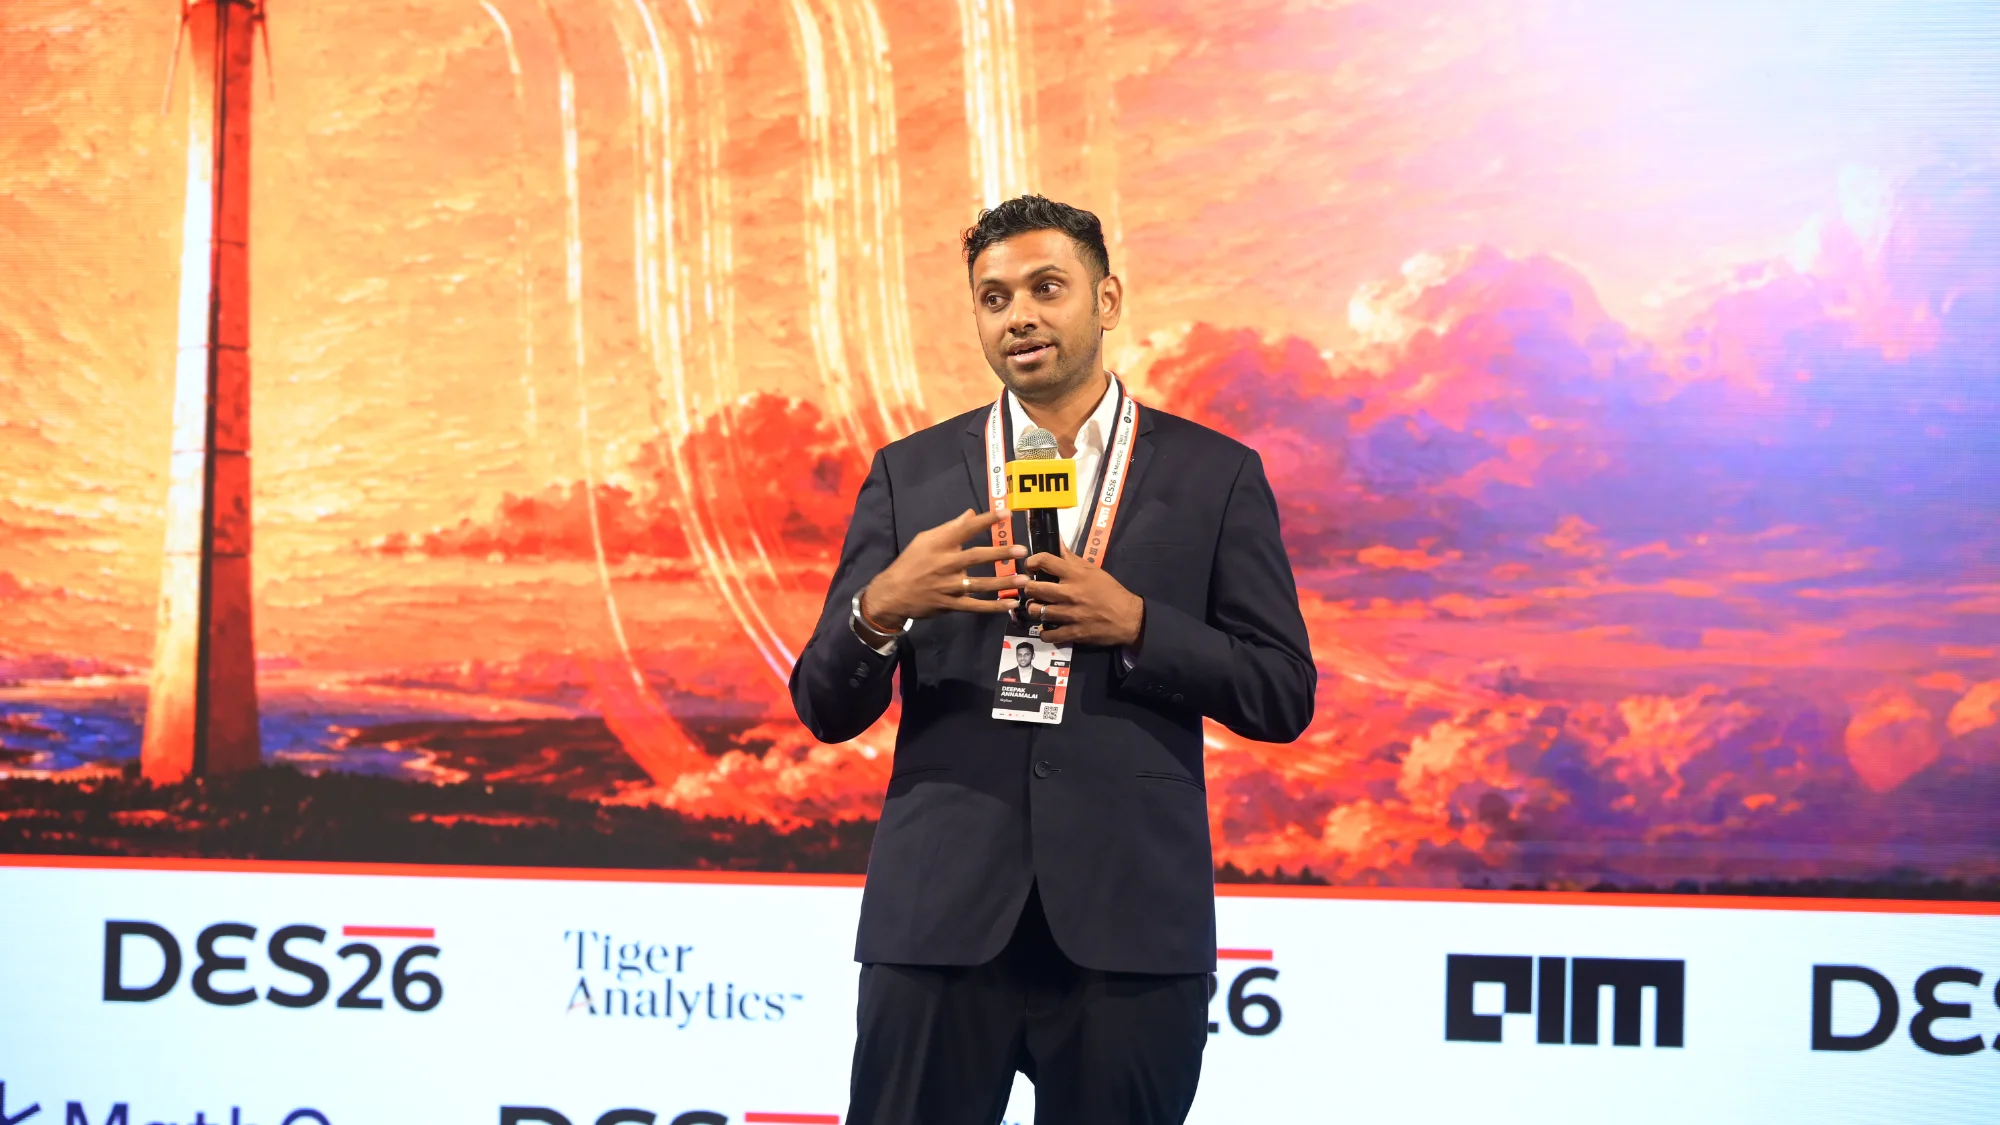
At the Data Engineering Summit 2026, organised by AIM, Deepak Annamalai outlines how enterprises are struggling to balance aggressive AI adoption with mounting concerns around privacy, compliance, and data security.
AI Knows More About Us Than Ever Before
Annamalai highlights that digital platforms already possess extraordinarily detailed behavioural profiles about consumers.
“Zepto and Swiggy know that my fridge is getting over before I know,” he says. “Uber knows where I am going across India. Hotstar knows whether I like action movies or Breaking Bad.”
Annamalai explains that AI systems are now moving beyond behavioural prediction into something far more intimate. “AI, which is now in almost all our phones, knows our personal secrets, our mood swings better than our wives and husbands,” he quips.
That hyper-personalisation has created immense business opportunities, but also unprecedented risks. According to Annamalai, the industry is approaching an inflexion point similar to the early days of banking, when people initially hesitated to trust institutions with their money. “Today it is a trusted ecosystem,” he says. “But it did not happen overnight.”
The same transition, he argues, now needs to happen for AI and personal data.
India’s DPDP Act Is Changing Enterprise Priorities
Annamalai describes India’s Digital Personal Data Protection Act as one of the world’s most prescriptive privacy regulations. Under the framework, companies must obtain explicit consent for different types of data usage, including AI training, personalisation, and marketing activities.
According to Annamalai, penalties for failing to properly protect sensitive data can reach ₹250 crore per violation. “In India, only when there is a fine, people do the right thing,” he jokes. The penalty stems from Section 8(5) of the DPDP Act, which requires companies to implement reasonable security safeguards to prevent personal data breaches.
It is expected to come into force once the law’s full compliance requirements take effect on May 14, 2027.
Annamalai emphasises that the regulation goes beyond consent management. The law also mandates strong technical protections around personal data. “It is actually saying you have to encrypt or tokenise the data in such a manner that if someone steals the data, then it becomes unreadable for them,” he explains.
The Real Problem is Data Sprawl
The core challenge, according to Annamalai, is not simply securing a single database. It is the uncontrolled replication of data across modern enterprise systems.
Data today flows across transactional databases, backups, replicas, ETL pipelines, analytics warehouses, AI systems, log files, and machine learning environments. Every copy becomes another attack surface.
“The data was collected from the customer only once,” Annamalai says, but it has since been replicated across countless systems, backups, pipelines, and AI environments.
The rise of agentic AI and MCP-based architectures is making this even harder to manage because data is no longer static. “The data is also going to constantly keep moving within the enterprise,” he says.
Skyflow’s Answer
Skyflow’s approach revolves around isolating sensitive data into what it calls a Data Privacy Vault.
The idea is to separate personally identifiable information (PII) from non-sensitive operational data. Sensitive information is stored inside a centralised vault, while the rest of the enterprise works using tokens instead of raw data.
Annamalai compares the approach to storing valuables in a bank locker instead of leaving them scattered around the house.
The tokenisation process replaces sensitive information with consistent surrogate values.
For example, a person’s name or phone number becomes a token that preserves the same format while hiding the actual value. “Deepak becomes D32, Nishant becomes N45,” Annamalai explains.
Because the tokens remain consistent, systems can continue performing joins, analytics, and downstream workflows without breaking schemas or APIs.
Why AI Changes Everything
Traditional masking and redaction techniques begin to fail once enterprises deploy generative AI systems.
Initially, companies tried blocking documents containing sensitive data entirely. That protected privacy but made AI systems less useful.
The next approach involved masking sensitive information using placeholders like ‘XXX’. But that degraded model quality because AI systems lost contextual understanding.
Skyflow instead developed what it calls entity-preserving tokenisation for AI workflows. Rather than deleting information, the system replaces it with contextual placeholders such as ‘name_01’ or ‘phone_01’.
The same entity always maps to the same token, preserving relationships and context for the model.
According to Annamalai, this enables enterprises to train and run AI systems without exposing raw sensitive data to models.
AI Models are Becoming a New Security Risk
Annamalai warns that enterprises are underestimating how dangerous AI systems themselves can become if not properly secured.
“Even if you host your AI model in your own AWS or GCP, the way these models function is very dangerous,” he says.
The challenge becomes especially severe with unstructured enterprise data such as PDFs, customer support tickets, payroll records, medical documents, and call transcripts.
Skyflow uses proprietary NLP systems to identify sensitive information across these formats before AI systems process them.
“It automatically finds those values and replaces them with a token,” Annamalai explains.
The company is already working with healthcare AI startup Hippocratic AI, which used Skyflow’s system to build healthcare-focused language models using medical records and doctor-patient notes while keeping sensitive information protected.
Privacy is Becoming Invisible Infrastructure
Annamalai stresses that privacy controls should not interrupt business workflows.
For example, Skyflow integrates with platforms like Snowflake, Databricks, and BigQuery through user-defined functions that dynamically restore sensitive information only for authorised users.
“As the user comes and does the query, looking at who he is and what permissions he has, the data gets transformed back like magic,” he says.
The goal is to ensure employees, AI agents, and analytics systems only see the minimum amount of personal information required for a task. This approach is already being adopted across enterprises, including Walmart, ServiceNow, Angel One, and Urbanic, according to Skyflow.
What’s Next?
India’s privacy regulations, combined with growing consumer awareness around data misuse, are forcing enterprises to rethink how information moves across systems.
“India was not privacy-conscious,” Annamalai says. “But all of us are becoming privacy-conscious.”
For AI companies, the challenge ahead is not merely building more intelligent systems. It is building systems that enterprises and consumers feel safe using at scale.

Your reaction
Discussion
What's your take on this story?
No comments yet — be the first to share your view.