Key takeaways
- GitHub launches Security Campaigns to tackle security debt and improve vulnerability remediation rates.
- Integrate Copilot Autofix for automated code suggestions and quicker fixes during security campaigns.
- Security managers can define and manage targeted campaigns to streamline vulnerability resolutions.
- Curate up to 1,000 code scanning alerts for focused remediation efforts using predefined templates.
GitHub announced, on Tuesday, the general availability (GA) of security campaigns with Copilot Autofix to help security and developer teams rapidly reduce security debt across their entire codebase.
The feature is available for all GitHub Advanced Security and GitHub Code Security customers. GitHub stated that security campaigns automate vulnerability remediation at scale, helping developer teams increase remediation rates from 10% to 55%.
The integration with Copilot Autofix accelerates remediation even further. As developers interact with campaign alerts in their pull requests, Copilot Autofix automatically generates code suggestions for fixes along with helpful explanations.
With Security Campaigns, security managers can draft security campaigns to refine the scope of the vulnerability resolutions before the work goes live. They can create GitHub issues, which can be updated automatically as the campaign progresses, and further track and manage remediation efforts.
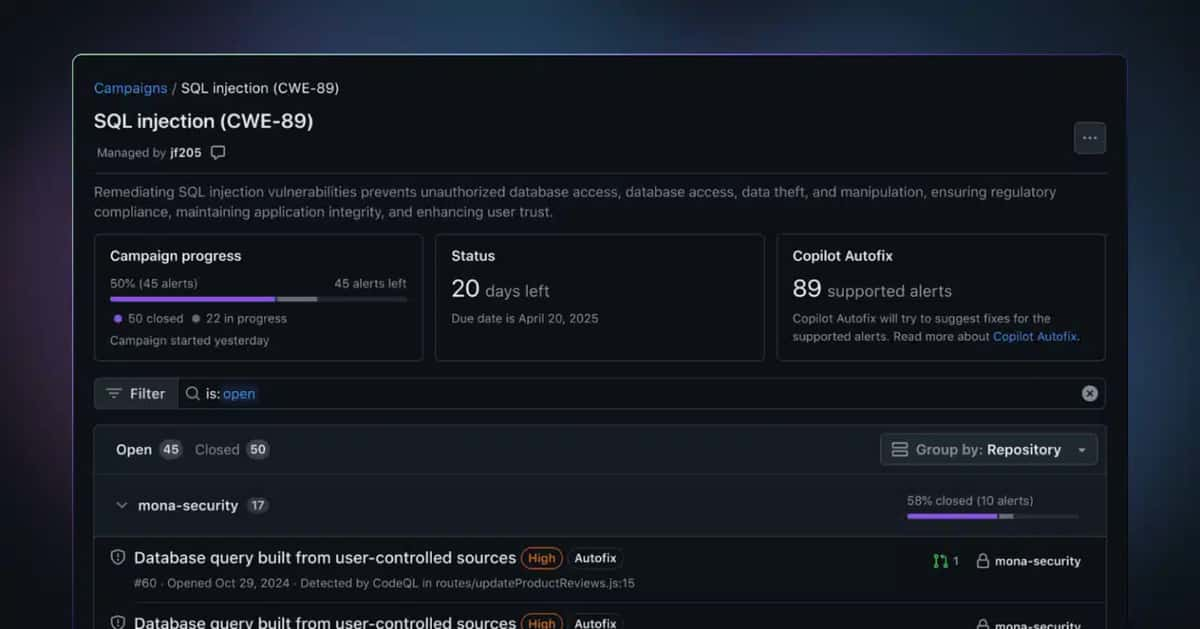
By bringing security experts and developers together within the familiar GitHub environment, Security Campaigns aims to streamline the entire vulnerability remediation process. Security teams can now curate and prioritise up to 1,000 code scanning alerts into targeted campaigns, utilising predefined templates based on common risks like the MITRE Top 10. This focused approach eliminates the time-consuming tasks of individual triage and prioritisation for developers.
Testimonials from early adopters like Jose Antonio Moreno, DevSecOps engineer at Lumen, highlight how Security Campaigns simplify life for developers. GP, a security engineer at Alchemy, praised the feature for educating their engineers about vulnerabilities, fostering collaborative fixes, and improving remediation time.
The company stated that they have observed organisations at various stages, where it has provided value for both developers and security teams in addressing security debt.
GitHub stated in its blog post that security debt is the biggest unaddressed risk that customers face, and 90% of risks are not prioritised. This is what GitHub’s Security campaign aims to change.