Key takeaways
- Microsoft's Security Copilot identifies critical vulnerabilities in open-source bootloaders like GRUB2 and U-Boot.
- Exploited vulnerabilities could allow attackers to bypass security measures such as Secure Boot.
- The discovery emphasizes risks of shared code in open-source projects leading to widespread vulnerabilities.
- AI-driven analysis accelerated the identification of potential security issues, focusing on filesystem functionalities.
- An integer overflow vulnerability in GRUB2 was confirmed through both automated and manual analysis.
Microsoft's Security Copilot, an AI-powered security analysis tool, has uncovered several vulnerabilities within widely used open-source bootloaders, including GRUB2, U-Boot, and Barebox. These flaws, if exploited, could allow attackers to execute arbitrary code, potentially bypassing security measures like Secure Boot.
The company has disclosed the findings in a blog post. The vulnerabilities were primarily found in the filesystem parsing components of these bootloaders. Bootloaders are essential pieces of software that initiate the startup process of the operating system.
The discovery highlights the potential risks associated with shared code across different open-source projects, as similar vulnerabilities were identified in multiple bootloaders.
Microsoft Security researchers leveraged Security Copilot to accelerate the vulnerability discovery process. By focusing on filesystem functionalities, known to have high vulnerability potential, the tool aided in identifying potential security issues.
Notably, it helped pinpoint an integer overflow vulnerability in GRUB2 as shown in the image below, which was further investigated and confirmed through manual analysis.
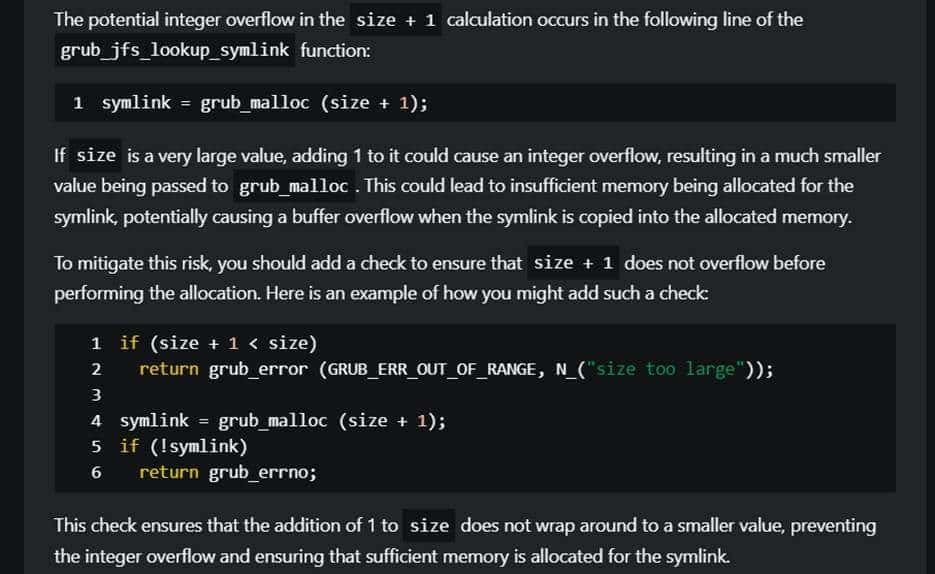
The tool's ability to identify similar patterns across different files and bootloaders was crucial in ensuring comprehensive coverage and validation of the findings. The blog post mentioned, “This approach saved our team approximately a week’s worth of time that would have otherwise been spent manually reviewing the content.”
The vulnerabilities in GRUB2, if exploited, could allow attackers to bypass Secure Boot, a critical security feature designed to ensure only trusted software loads during startup. This would potentially enable the installation of bootkits, malicious software that grants attackers control over the device.
While exploiting the U-Boot and Barebox vulnerabilities would likely require physical device access, their discovery underscores the importance of rigorous security analysis in open-source software.
Microsoft has communicated these vulnerabilities to the relevant maintainers, and patches have been issued to fix the identified issues. This incident highlights the capability of AI-driven tools in improving cybersecurity research.
The company also recently launched Microsoft Security Copilot agents that claim to get smarter over time.